Too small to be a target? Automated attacks don't check size
Think your business is too small to attack? Automated attacks sweep every address for gaps. What PHP2Shell showed, what the numbers say, and where to start.
 By Jeensuk Yang
PHPFree · Web security · Column
?Who this is for
- You run a small business and feel no one would bother attacking you
- You saw the PHP2Shell news and filed it under "big-company problem"
- You want facts, not scare stories, before you decide anything
!What you'll learn
- How today's automated attacks actually choose where to go
- What the numbers say, and what they don't
- Why "not us" feels true, and the one-minute check to start with
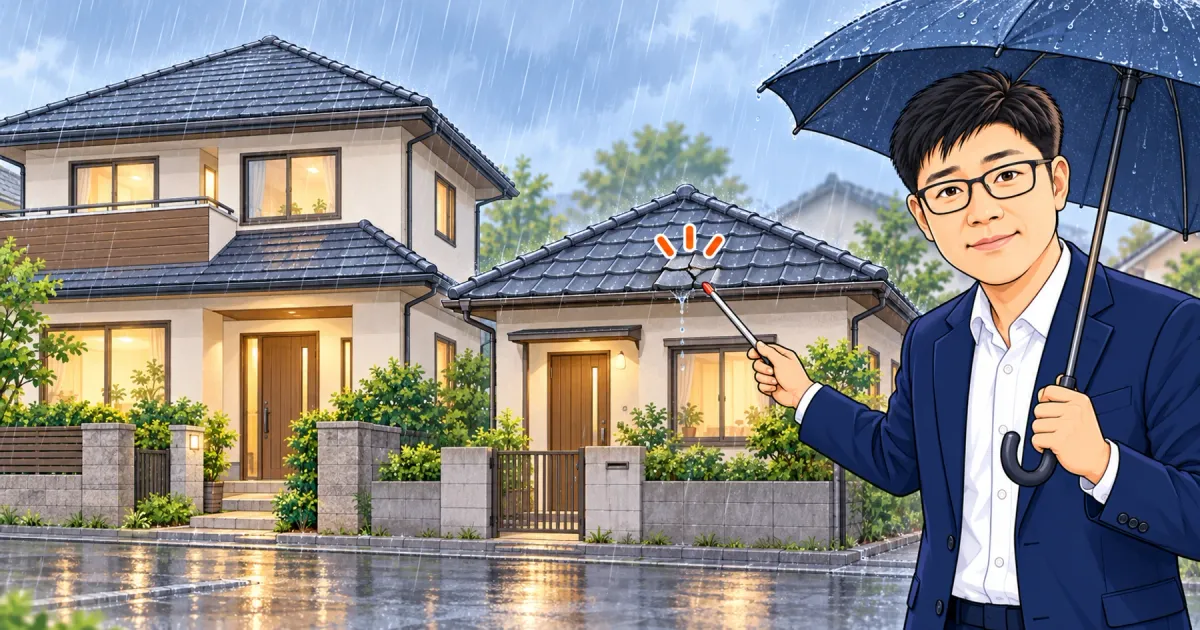
Rain doesn't check the size of the house. It checks for gaps.
In a storm, the house that leaks isn't the big one. It's the one with a gap. A mansion with a sound roof stays dry; a small house with one cracked shingle gets wet. "Who would target a company our size?" I've thought that myself, running a business. It's not a foolish thought. But today's attacks rarely start with a person choosing a company, and I'll show you that with facts and numbers.
Do attackers really skip small companies?
There's little evidence that being small gets you skipped. Most of today's attacks come for an internet address and the gap at that address, not for a company's name.
The old-time burglar chose a house. He checked how high the wall was and whether the family looked wealthy, then waited for night. Today's attack programs are different. They're like a machine that walks down the street trying every door handle in turn. They don't read the name on the mailbox. They only check whether the door opens.
- Attackers pick a company
- Big, rich companies come first
- We're too small to be noticed
- Programs sweep addresses in order
- The first door that opens gets used
- Small sites with gaps are fair game
So the question changes. Not "Are we worth targeting?" but "Is our door locked?"
Jeensuk's take"Who would target us?" has no answer. "Is our door locked?" does.
How did automated attacks actually behave this time?
From the first day PHP2Shell was public, attack programs sent the same requests to servers everywhere, without regard to who owned them. A US security firm and Cloudflare recorded it.
VulnCheck runs decoy servers, called canaries, to watch attacks. On October 21, 2026, the day PHP published the fix, it reported that one source address "connected to 188 canary hosts" and another to 26, sending file-upload requests "on hosts in several cloud regions and providers."1
Cloudflare said "the vulnerability was leaked before the official release date and we observed attack traffic targeting our customers."2
We expect to continue seeing widespread exploit attempts with public PoCs. — VulnCheck, Oct 21, 2026
A decoy server is an empty house with no name on it. It has no company name and no revenue. The door handles were tried anyway, which tells you the programs don't look at who lives there.
Jeensuk's takeTo an attack program, your website isn't "a small company." It's "one address." And everyone has one.
What do the numbers say, and what don't they say?
The numbers show cybercrime is large and that unpatched software is a leading way in. They don't show that small businesses are hand-picked. What they show is that there's no evidence size keeps you out.
| Source | What it found |
|---|---|
| FBI IC3, 2025 (as reported by CyberScoop) | "More than 1 million complaints" and losses of "almost $20.9 billion" in 20253 |
| Verizon 2026 DBIR | 31% of breaches now start with software vulnerabilities, beating stolen passwords as the top way in4 |
| W3Techs, Oct 24, 2026 | PHP runs 69.3% of websites whose server-side language is known5 |
And PHP is under a large share of the web, as of October 25, 2026. This vulnerability isn't a big-company story. It sat under the floor of a great many business websites.
Jeensuk's takeI won't inflate the numbers. But there aren't any numbers that back up "we're small, so we're fine," either.
Why does "it won't happen to us" feel so true?
People tend to believe bad things are more likely to happen to others. Psychologists call it optimism bias. It's not a failing; everyone has it.
In a 1980 study, the American psychologist Neil Weinstein showed that people expect bad events to happen to them less often than to others.6 It shows up in business too: in a 2025 survey of 1,000 executives at organizations with under $100 million in revenue, 64% said their organization is "too small to be an attractive target."7 And the hacks in the news are always famous big companies. A small company's breach doesn't make headlines, so there's no picture of it in our heads.
Jeensuk's takeThere's no need to blame yourself for thinking "not us." Just turn that thought into one quick check.
So what should you check first today?
Start by finding out whether your site is affected by this vulnerability. It takes a minute. Decisions come after.
The first step against a machine that tries every door isn't fear. It's knowing what kind of lock is on your door.
- See if you're affected: take the one-minute check, five questions that sort you into "Not affected," "Needs checking" or "Needs action" (English edition coming soon).
- Read your host's notice: on shared or managed hosting, many hosts applied the fix for you. Hostinger, for example, said every plan except VPS needed no action.8
- Ask one question: ask your developer or whoever manages the site, "What PHP version are we on, and has the fix been applied?"
- Look for traces: if you worry someone got in before the fix, see the web shell self-check (English edition coming soon).
If it all comes back "Not affected," that's a great result too. Peace of mind you checked for weighs more than peace of mind you guessed.
Jeensuk's takeA small company's strength is that it can check fast and decide fast. Today, it takes a minute.
Frequently asked questions about small businesses and automated attacks
Our website has nothing worth stealing. Is it still at risk?
It can be. Automated attacks look for doors that open before they look at what's inside. Check whether your site is affected before you worry about what's on it.
Does this mean small businesses get attacked more?
That's more than the data shows. This article only says there's no evidence that being small keeps you out.
Isn't shared hosting enough to keep us safe?
For this PHP fix, many hosts applied it for their customers. But if you manage your own server or run an old, unsupported version, it's different, so check your host's notice.
SOURCES
- VulnCheck, "PHP2Shell Vulnerabilities: CVE-2026-109618 and CVE-2026-109619" (Oct 21, 2026) vulncheck.com
- Cloudflare, "Cloudflare deploys protections against php2shell vulnerability" (Oct 21, 2026; updated Oct 23) cloudflare.com
- CyberScoop, "Cybercrime losses jumped 26% to $20.9 billion in 2025" (Apr 7, 2026, reporting on the FBI IC3 2025 Internet Crime Report) cyberscoop.com
- Verizon, "2026 Data Breach Investigations Report" verizon.com
- W3Techs, "Usage statistics of PHP" (Oct 24, 2026) w3techs.com
- Wikipedia, "Optimism bias" (Weinstein 1980, Journal of Personality and Social Psychology 39(5), 806–820) wikipedia.org
- Security Boulevard, "Survey Surfaces Myriad Small Business Security Challenges" (Coalition / Wakefield Research survey, Jul 7, 2025) securityboulevard.com
- Hostinger, "Hostinger deploys protections against php2shell PHP vulnerabilities" (Oct 21, 2026; updated Oct 23) hostinger.com
Once you know it's your story too, the next steps continue here. More English editions are on the way.
- Too small to be a target? Automated attacks don't check your size (this article)
- Is your business website affected? A one-minute PHP check (coming soon)
- What is PHP2Shell? What it means for your business website
- PHP vulnerability fix guide: from checking to moving off PHP (coming soon)
More articles on the ATATAKAI Digital blog.
Is your door locked? See in 30 seconds.
Enter your site address and we'll tell you right away whether it runs on PHP and where your host stands. If you're not affected, we'll say so plainly: "No need to move right now."
Run the free 30-second checkWant to talk it through after you see the result? Contact ATATAKAI Digital
Updated 10月 25, 2026